Summary
Storage is often one of the most underprotected parts of an environment. To close this gap, Pure Storage and CrowdStrike have developed the industry’s first direct, API-driven integration between storage and security, transforming storage into an active, intelligent part of your cyber defense strategy.


The digital enterprise is accelerating, fueled by the rapid rise of cloud computing, AI, edge technologies, and IoT. This transformation is reshaping how organizations operate—but it’s also amplifying the complexity and vulnerability of the digital landscape. Highlighting this growing threat, Cybersecurity Ventures projects that global ransomware damages alone will reach a staggering $57 billion in 2025.
Cyberattacks are persistent, adaptive, and inevitable. It is no longer a question of if, but when and how severe the impact will be.
While many organizations have invested heavily in strengthening endpoint, network, and identity security, one critical layer remains largely overlooked: data storage. It’s where your most valuable assets reside—yet it remains one of the least integrated into modern cyber defense strategies.
At Pure Storage, we’ve reimagined what it means to defend your most critical asset: your data. Through a deep integration with CrowdStrike’s industry-leading next-gen SIEM and Falcon Fusion SOAR, we’ve transformed storage from a passive target into an active, intelligent participant in your cyber defense strategy—delivering real-time visibility, automated response, and rapid recovery at the data level.
Why Storage Is the Blind Spot in Cybersecurity
Despite advancements in endpoint, identity, and network security, data remains the ultimate target for cyberattackers. And yet, the storage infrastructure that holds that data is often treated as an operational layer—not a security layer. This makes it one of the most underprotected parts of the environment.
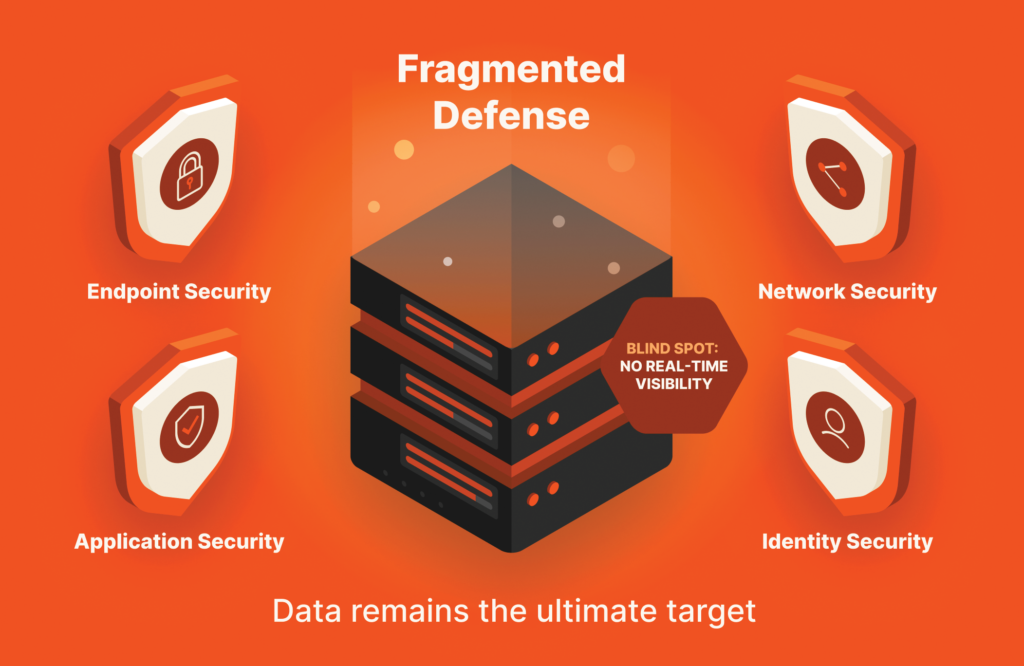
Figure 1: When defenses don’t connect, data becomes the easiest target.
Traditional storage systems introduce risk because they are:
- Isolated from security tools: Storage has historically operated in a silo, with little to no integration into modern SIEM or SOAR platforms.
- Lacking real-time visibility: Security teams are often blind to what’s happening on storage until it’s too late.
- Dependent on manual recovery: Restoring data after an incident is typically slow, reactive, and operationally disruptive.
A delay in detection and response can mean the difference between a minor incident and a catastrophic breach.
Breaking New Ground: Pure Storage + CrowdStrike Joint Cyber Defense
To close one of cybersecurity’s most overlooked gaps, Pure Storage and CrowdStrike have developed the industry’s first direct, API-driven integration between storage and security. This makes Pure Storage the first storage partner to embed natively within the CrowdStrike Falcon platform.
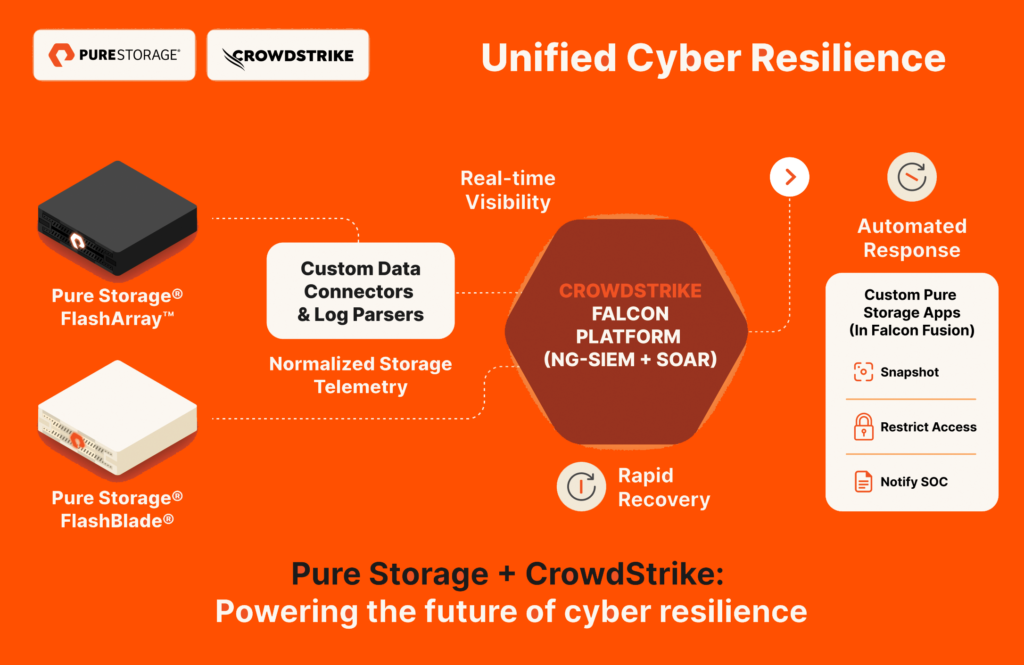
Figure 2: Turning storage into a first-class citizen of cyber defense.
But this integration is far more than a connector. It represents a closed-loop, automated defense framework that transforms storage from a passive infrastructure layer into an intelligent and active first responder. By unifying data and security operations into a single, orchestrated fabric, organizations can now detect, respond, and recover faster—making infrastructure a core component of modern cyber resilience.
Direct API-driven Integration
A simple log-forwarding connector is no longer enough. True resilience requires native, bi-directional communication between security and storage.
Through its direct API integration with the CrowdStrike Falcon platform, Pure Storage enables real-time orchestration that goes beyond monitoring. Falcon can now directly command storage arrays to take protective actions—such as restricting access or creating immutable snapshots.
This level of native integration marks a fundamental shift in how organizations defend against threats. Instead of passively observing, storage becomes an active layer of protection and a cornerstone of the closed-loop defense model.
Data Ingestion and Correlation
Storage telemetry is often complex and difficult for analysts to interpret. Pure Storage solves this by enabling seamless ingestion and enrichment of storage data into the CrowdStrike ecosystem:
- Custom data connectors for FlashArray™ and FlashBlade® securely forward structured logs.
- Specialized log parsers normalize unstructured telemetry, transforming it into rich, contextual signals.
These signals are then ingested into CrowdStrike’s next-gen SIEM, Falcon LogScale, where they are correlated with endpoint and network intelligence. The result is a high-fidelity threat signal that gives security teams immediate, actionable visibility into storage-level events—connected to the broader attack landscape.
Automated Response with CrowdStrike Falcon Fusion SOAR
The real power of this integration lies in its ability to automate response.
Custom Pure Storage apps for FlashArray and FlashBlade are embedded within CrowdStrike Falcon Fusion SOAR, providing a library of pre-tested, validated operations. These modular building blocks allow security teams to create playbooks that act directly on storage endpoints—without manual intervention.
With these automated workflows, organizations can:
- Instantly trigger immutable SafeMode™ Snapshots
- Restrict or revoke user access to compromised systems
- Contain threats before they spread
This zero-touch automation significantly reduces risk, minimizes response time, and ensures the system responds faster than attackers can move.
The following table provides a summary of these core technical components, their functions, and their resulting strategic benefits:
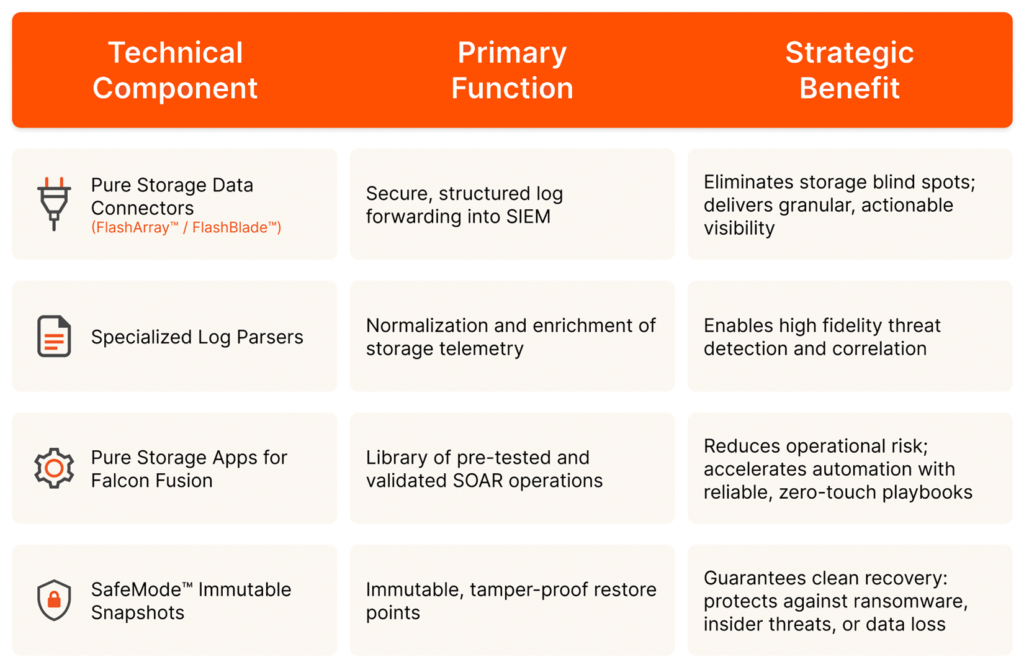
Figure 3: Core Pure Storage security components, their functions, and strategic benefits.
Now, security teams can see storage events in the same window as endpoint activity, providing a complete picture of an attack kill chain and enabling an immediate, coordinated response.
From Raw Alerts to Automated Response: Storage-centric Defense in Action
In the world of cybersecurity, security teams are flooded with a constant stream of alerts. The challenge isn’t just the volume, but the nature of the data itself. Raw logs are often cryptic, complex, and difficult for a human analyst to interpret quickly, making it tough to understand the situation and take decisive action when every second counts.
Consider a typical raw alert from a storage system:

Figure 4: Unparsed storage alert showing real-time alert data from Pure Storage.
For an analyst under pressure, this single line is dense and slow to act on. The critical information is there, but it’s buried in text that isn’t designed for immediate human comprehension. This delay between detection and response is where attackers gain the upper hand.
Bridging the Gap from Cryptic Logs to Actionable Intelligence: How Pure Storage Helps
This is precisely the problem the Pure Storage and CrowdStrike integration solves. The solution begins with custom-built Pure Storage data connectors for FlashArray and FlashBlade.
Instead of just forwarding raw logs, these connectors perform two critical functions:
- Ingestion: They seamlessly pull all relevant telemetry directly from the storage systems.
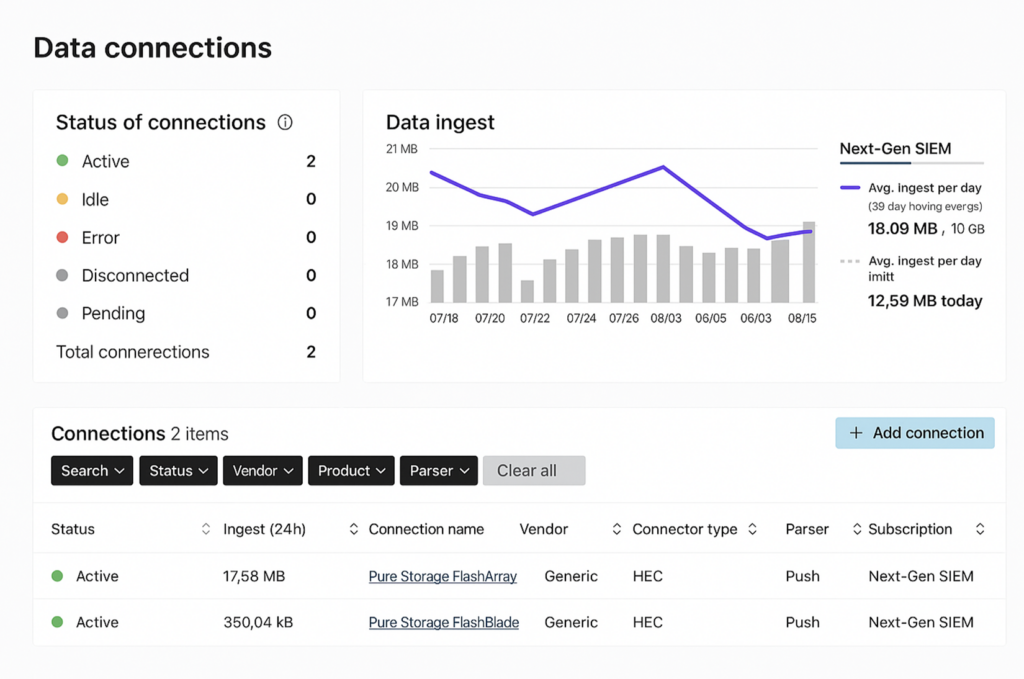
Figure 5: Data connectors ingesting telemetry from Pure Storage® FlashArray and FlashBlade.
- Parsing: Using a custom-developed parser, they instantly translate the raw logs into a structured, human-readable format. Critical components like severity, array name, message code, and a clear summary are categorized into standardized fields.
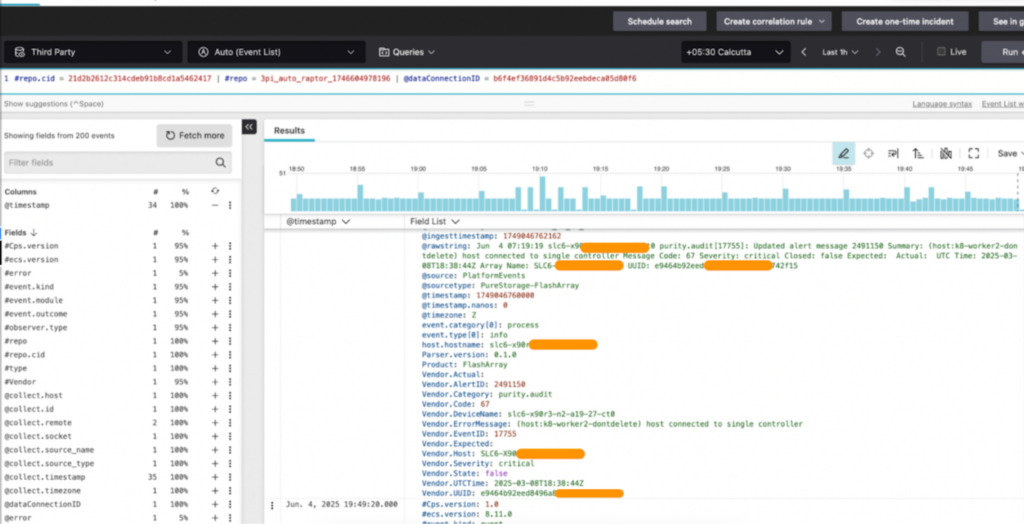
Figure 6: Parsed storage alert displaying structured real-time data from Pure Storage.
These readable, categorized events become high-fidelity signals that can trigger automated workflows in CrowdStrike Falcon Fusion SOAR using the custom Pure Storage SOAR apps.
Putting It Into Practice: Real-world Use Cases
Scenario 1: Ransomware Containment
An attack begins on an endpoint and attempts to encrypt data on a connected storage volume. The rapid randomization of data causes the storage array’s data reduction ratio to plummet, triggering a high-severity alert.
Automated response:
- A SOAR playbook is instantly activated, triggering a SafeMode immutable snapshot of the affected volume, preserving a clean, unencrypted restore point.
- Access to the volume from the compromised host is automatically restricted to prevent further damage.
- The SOC team is alerted with a complete incident timeline, enabling rapid recovery from the clean snapshot.
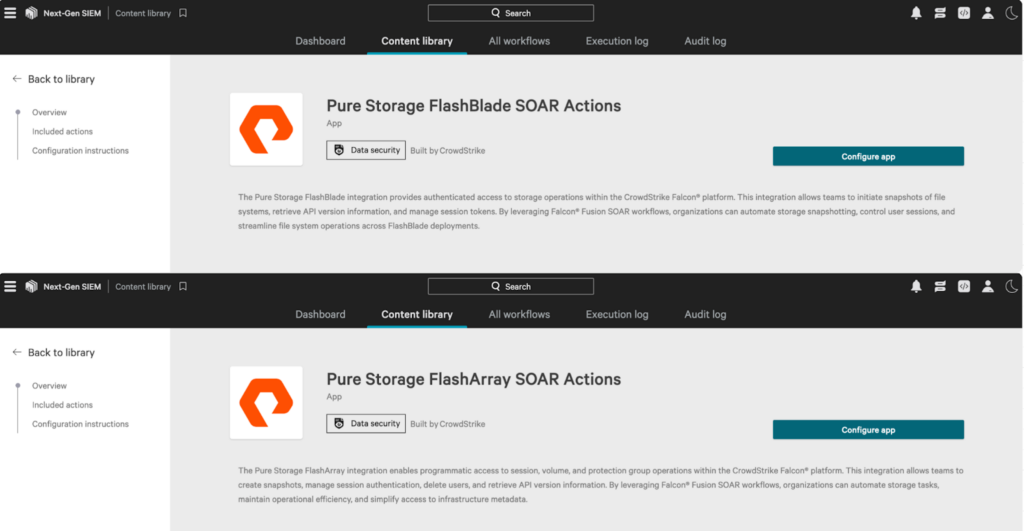
Figure 7: Pure Storage SOAR app available on the marketplace and accessible for users.

Figure 8: Workflow execution example.
Scenario 2: Insider Threat Mitigation
An internal user account begins downloading an unusual volume of sensitive files, triggering an anomaly detection alert based on their normal access patterns.
Automated response:
- An immutable snapshot of the filesystem is taken to preserve a forensically sound copy of the data.
- The user’s access to the sensitive data is restricted to read-only or blocked entirely.
- An alert is sent to the security team with a detailed activity timeline for investigation, preventing further data exfiltration.
In both scenarios, SafeMode Snapshots serve as the ultimate defense. They create point-in-time copies of your data that cannot be altered, deleted, or encrypted—even by an administrator with full credentials—guaranteeing you always have a clean state to recover from.
- Restrict access to compromised areas
- Notify the SOC and initiate incident workflows
What This Means for Your Business
By embedding Pure Storage into the heart of your CrowdStrike-powered security operations, you unlock:
- Accelerated detection and response: Eliminate blind spots and see the full picture of your infrastructure—in real time.
- Granular visibility: Understand not just what happened, but where, how, and precisely what data was impacted.
- Proactive risk and downtime reduction: Contain attacks quickly, preserve data integrity, and maintain business continuity without delay.
Final Thoughts: The Future Is Resilient
The traditional cybersecurity approach—focused solely on perimeter defense—is no longer sufficient in a landscape where threats evolve rapidly and strike deeper into the data layer.
With the integration of Pure Storage and CrowdStrike, we’ve taken a critical step toward bridging the long-standing gap between security and storage. By enabling automated snapshot creation, dynamic access control, and targeted user delegation, this integration empowers security teams to respond swiftly; limit blast radius; and maintain clean, restorable states—all without slowing down the business.
This marks a fundamental shift from reactive defense to proactive resilience. For modern cyber resilience to succeed, storage can no longer be a passive bystander; it must be an active, integrated component of the security architecture. It’s no longer about simply reacting to threats—it’s about building an intelligent, self-defending data infrastructure that is inherently more aware, responsive, and resilient by design.
Shield Your Organization from Data Loss
Learn how Pure Storage technology keeps businesses protected from cyberattacks.